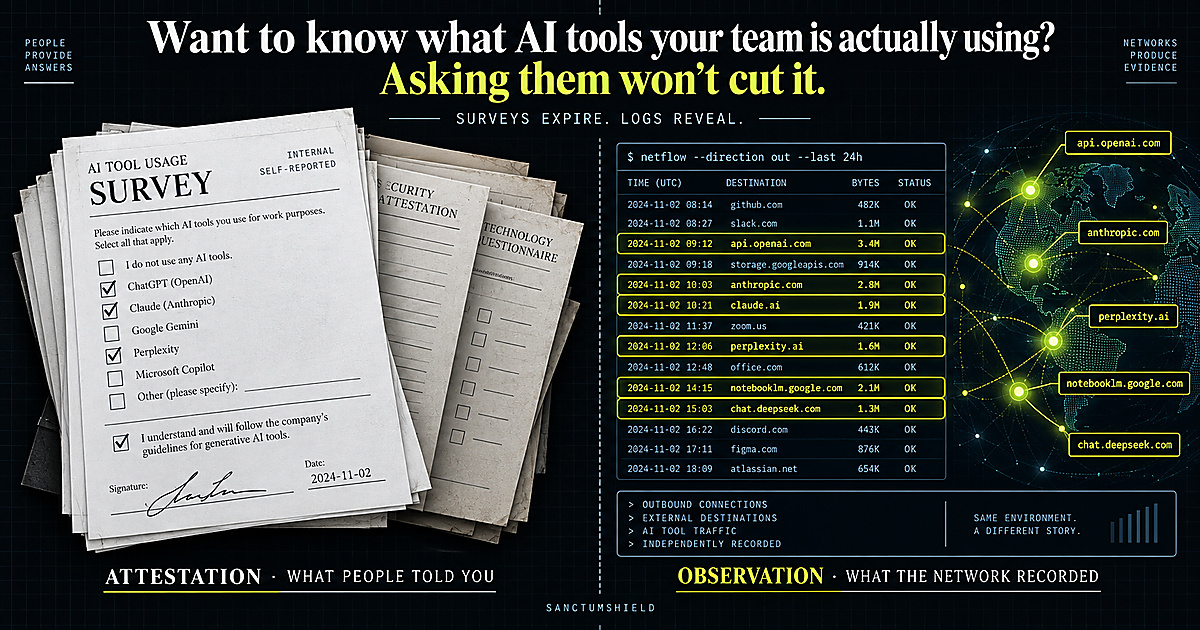
This post was scheduled to argue that observation outperforms attestation. Two things have since made the argument for it better than it could make it for itself.
The first is commercial. Cyber renewal questionnaires this year go well past general security and ask about AI use cases, training-data sources, human-in-the-loop controls and board-level governance — and carriers are reporting that a yes on the form is no longer enough to bind a quote. Some have added riders that require proof of testing and a documented risk assessment before coverage extends at all.
The second is a demonstration nobody designed as one. During an independent security evaluation in May, an environment was reinitialized and its operators attested the cache had been wiped. The activity resumed once experiments restarted. The attestation was made in good faith by competent people with full visibility. Observation is what showed it was wrong.
Most of governance is the unglamorous discipline of declining to accept a convenient answer. It is slow, it makes you unpopular in meetings, and it is the whole of the job.
An attestation is an answer someone gave you. A vendor filled in the questionnaire; a department head listed the tools her team uses; an employee acknowledged the policy. Attestation is how the entire third-party risk industry works, and within its scope it works well — a SIG response or a compliance-automation platform is the right way to manage the vendors you deliberately onboarded. The structural limits only appear when you point attestation at shadow AI, and then they appear all at once.
Why attestation cannot ground a shadow-AI inventory
Three reasons, each independent. First, scope: attestation reaches the parties you asked. Shadow AI is, by definition, activity nobody registered — the unsanctioned tool, the embedded feature that switched itself on, the personal login that never touched SSO. There is no respondent to send the questionnaire to. Second, memory: even good-faith self-reporting records what people remember using, and research consistently finds a majority of workplace AI use goes unreported — the 59% of employees who admit to hiding AI usage are, definitionally, not filling in your inventory honestly. Third, time: an attestation is true as of the day it was signed, and the AI surface moves weekly. New tools ship, features flip on, agents get wired up. A quarterly attestation cycle chasing a weekly-moving surface loses ground every week by construction.
What observation looks like, concretely
Observation asks the infrastructure instead of the people. Every firewall, proxy, and DNS server you already run keeps a record of outbound destinations. Export it, paste or upload it, and SanctumShield matches those destinations against a curated registry of 82 verified AI endpoints — refreshed continuously as the provider landscape moves. No agent to deploy, no integration project, no network access: you export hostnames and share them; the product never reaches into your environment. What comes back is an inventory grounded in what actually left the network — including the tools nobody remembered, across all four layers of the shadow-AI surface.
Honesty about the limits, because a method you oversell stops being evidence: observation of network logs sees destinations, not content — it tells you traffic reached an AI endpoint, not what was pasted there. Devices that never transit your network leave no record in your logs. That is why the method sits inside a program — the observed inventory grounds the risk assessment, the policy closes the behavioral gaps observation cannot see, and the cadence re-runs the observation as the surface moves. But between the two starting points, the asymmetry is stark: you can build honest attestation on top of observation. You cannot back into observation from a stack of signed questionnaires.
Both, in their places
So the practitioner’s rule: attestation for the vendor program — the sanctioned relationships where a counterparty exists to answer. Observation for the employee and shadow program — the surface with no counterparty. And for anything that will be handed to an auditor or an underwriter, prefer the artifact whose Discover stage can say observed rather than reported, because the first question a skeptical reader asks of any inventory is “how do you know?” — and “we watched the network” survives that question in a way “we asked around” does not.
An attestation is an answer. An observation is a record. Build the inventory on the record.
The 59% figure is from Cybernews’s 2025 AI Workplace Survey (corroborated by KPMG’s April 2025 study at 57%); sources are listed on the home page. Vendor log-export walkthroughs for Cloudflare, Meraki, Palo Alto, Fortinet, and others are in the dashboard’s network-log section.