There is no cheap version of this decision. Governing a surface that changes monthly, under obligations that are already in force, is expensive whichever way you go about it. What varies is whether the money buys you a document or a program, and that difference compounds every quarter afterwards.
If you hand a Big 4 firm your AI-governance problem, you will get back serious work: interviews, a current-state assessment, a gap analysis, a roadmap, and a polished report. For a large, complex enterprise with the budget and a dedicated program office to operationalize it, that can be exactly right. This piece is not a knock on the work. It’s about what happens to that work the day after it’s delivered.
Start with the concession, because it is a real one
In December 2025, KPMG International became the first Big Four international entity to certify its own AI management system to ISO/IEC 42001, audited by Schellman, following member firms in Australia, Spain, India and the United States. Their own stated reason is the right one: “You can’t guide clients on an AI journey you aren’t on yourself.” Deloitte, PwC and EY have all made comparable investments in responsible-AI practice.
So this is not an argument that the Big 4 do not do AI governance, or that they do it badly. They do it, they are certified in it, and for a large enterprise with a program office to operationalize the output, an engagement can be exactly the right purchase.
The distinction is narrower, and it survives the concession intact. A certification covers their management system. An engagement produces a document about yours, describing it on the dates the work was done. Those are different objects, and only one of them is what an auditor asks you for.
What the engagement actually is
A typical AI-governance advisory engagement runs for a defined number of weeks against a fixed scope and ends in a deliverable, frequently a slide deck and a written assessment. The published ranges vary so widely by scope and firm that quoting one is not useful; what matters is the shape, not the price. Three things follow from that structure, and none is a criticism of the consultants:
- It is point-in-time. The assessment describes your AI surface and your regulatory exposure as they were during the engagement window.
- It is a deliverable, not a system. A report tells you what to do; it doesn’t keep itself current or produce the ongoing evidence.
- It is re-purchased, not refreshed. When the picture changes, you scope another engagement — another six figures, another six to twelve weeks.
Why a snapshot fails at AI governance specifically
AI governance is not a domain where a snapshot ages gracefully. The AI surface changes monthly: an embedded AI feature flips on inside a SaaS tool you already pay for, three new agents get wired to company data, an employee adopts a tool that didn’t exist at kickoff. The regulations move too — the EU AI Act’s obligations phase in on their own calendar, Colorado’s SB 26-189 arrives January 1, 2027, and delegated acts keep shipping. A governance assessment written in Q1 is, through no fault of its authors, a historical document by Q3.
This is the difference between Due Care and Due Diligence. Due Care asks whether you put reasonable safeguards in place — a good engagement demonstrates that on the day it ships. Due Diligence asks whether you are continuously verifying they still work — and a slide deck cannot. A PowerPoint is an argument that you were careful once. It is not evidence that you are still governing.
The durable artifact is a program, not a report
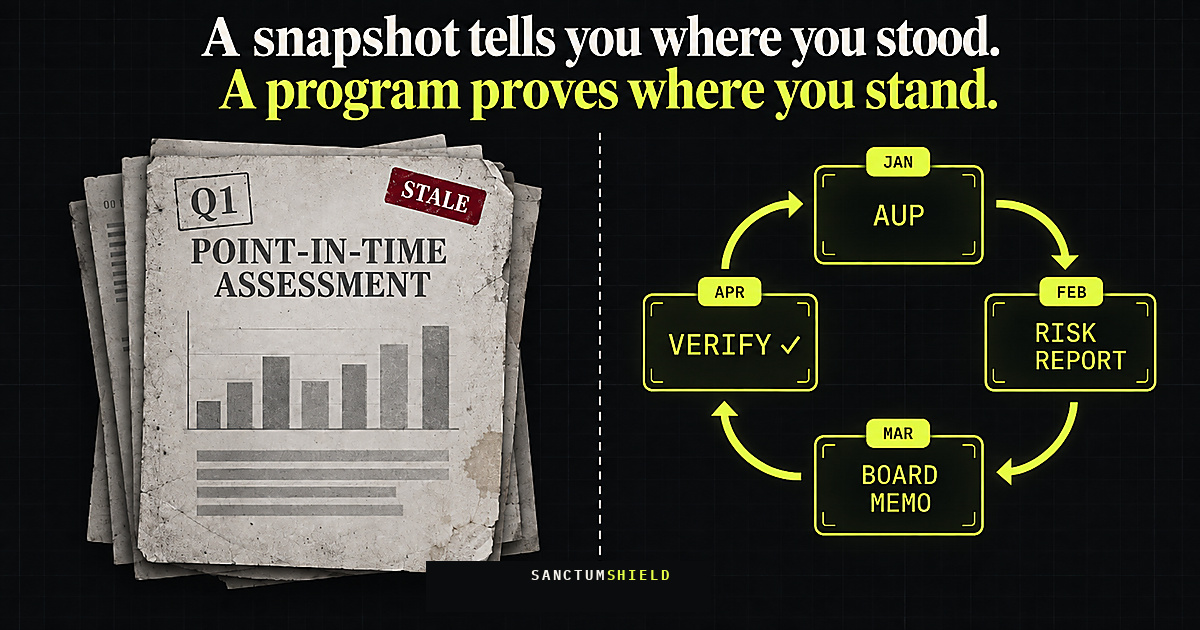
What survives an auditor, an underwriter, and a board across time is not the best single assessment — it’s a continuously-maintained program that re-runs as the AI surface and the regulations change, and produces the living artifact chain each time: a regulation-anchored AUP, a documented risk assessment of the AI actually in use this month, an Executive Risk Report and board memo, and a verification URL. The value isn’t the document; it’s that the document is never stale.
For a 50–2,000-employee company, the economics settle it. A six-figure engagement every time the picture moves is not a program — it’s a series of snapshots with gaps between them. A subscription that refreshes the citations, the endpoint registry, and the risk picture every month, and regenerates the artifact on demand, is the program — at a fraction of a single engagement’s cost. Where you genuinely need bespoke human advisory (a novel model-risk question, an M&A diligence), buy it — but buy it on top of a living program, not instead of one.
A great assessment tells you where you stood. A program proves where you stand.
Engagement cost and duration ranges reflect published Big-4 AI-governance advisory pricing; the full cost comparison and its sources live on the SanctumShield home page and in Beyond SIG Lite. The monthly-refresh commitment behind “never stale” is documented on the What’s New page.